Event Recap
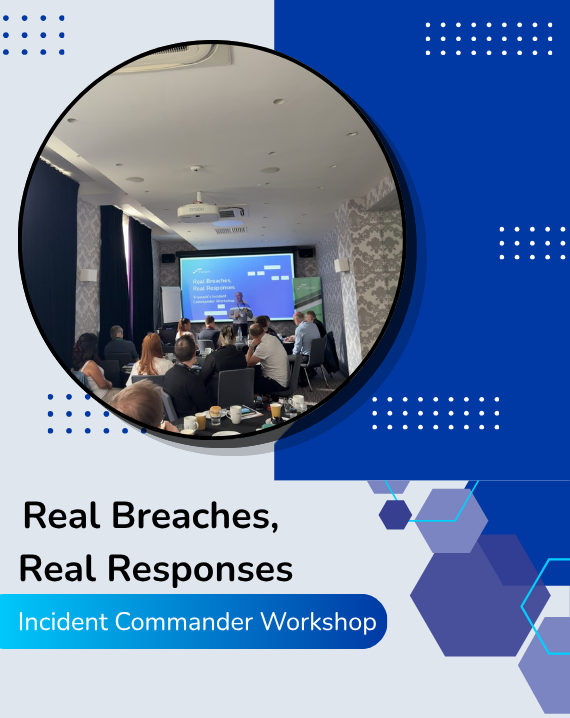
It was a pleasure to welcome our cybersecurity minded guests to our Incident Commander Workshop at the Malmaison Hotel in Newcastle.
In this workshop we brought the realities of being on the receiving end of a cyber-attack to life. Our Chief Technical Officer, Russell Henderson walked guests through real breaches that we helped local organisations contain and recover from, without a single ransom paid.
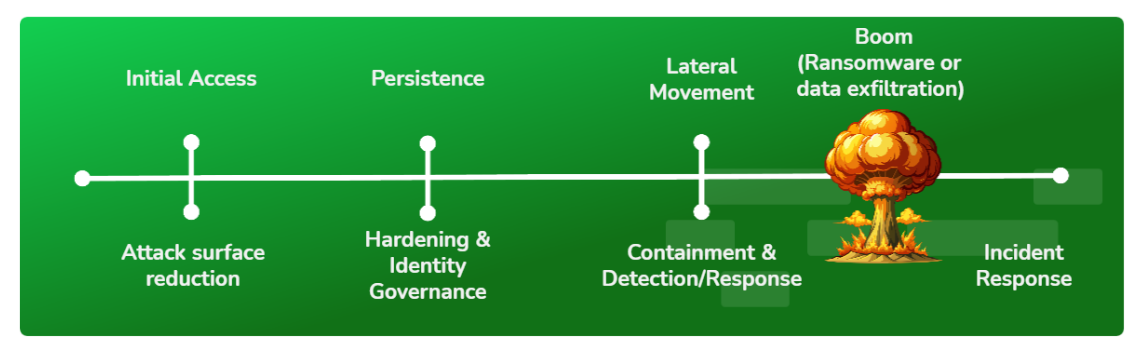
To kick off the workshop we introduced the concept of “keeping left of boom; the boom in question being a successfully executed breach by threat actors.
At the highest level, every action you take to secure your business and prevent cyber threats puts you further left of boom. Incident response is the last resort, the more steps taken left of boom the lower the likelihood and impact of a boom.
After establishing the unanimous goal prevent breaches rather than responding to them, we asked one question, “You’ve been breached, what are the first 3 things you do?”.
Immediately sparking debate among attendees, the addition of a 60 second timer brought the issues of decisions by committee in the time sensitive environment of a breach to the forefront.
The valuable discussion then identified some solid first responses and importantly, raised more questions like, “How do you communicate if your work comms channels are down?” and “Who knows the policy and contact details for your cyber insurance company?”.
The core of the workshop was the 2 real breaches against local North East businesses, that Trustack’s Incident Commander and his team had contained and recovered.
While the companies remained completely anonymous, we pulled back the curtain on the technical detail of each attack from initial access to containment and recovery; showing the direct effect of having the correctly configured security tooling and processes in place.
Walking through the breaches raised numerous valuable questions for attendees to ask of their businesses, and they didn’t leave empty-handed…
Everyone who joined us for the workshop received a list of 18 questions centred around response readiness, security posture and business continuity to takeaway and ask of their business, with some already building breach response plans as a result.
Thank you again to everyone who joined us for the day!
If you’d like the 18-question handout from the event, contact us today.
To provide the best experience on our site, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behaviour or unique IDs on this site.